

Australia 11th in Microsoft cyber report as phishing rises
Mon, 19th Oct 2026 (Today)
Microsoft has released its 2026 Digital Defence Report, which shows Australia ranked 11th globally in the first half of 2026 among countries where customers were most frequently affected by cyber activity.
The report identifies three main trends shaping the threat landscape: attacks are becoming more interconnected across identities, applications, cloud environments, suppliers and critical infrastructure; artificial intelligence is increasing the speed and scale of cyber activity; and compromised identities remain a common route into broader attacks.
Microsoft's figures point to a marked rise in phishing, which accounted for 23% of observed intrusions in 2026, up from 7% a year earlier.
It also found that more than 52% of intrusions involving compromised accounts led to further credential theft, underscoring how quickly a single breach can spread through an organisation. In another sign of pressure on defenders, the time between vulnerability discovery and weaponisation can fall to less than 24 hours.
Australian exposure
The findings place Australia within a broader global pattern of faster, more connected attacks. Incidents are increasingly moving across multiple systems and organisations, shifting the focus from prevention alone to resilience and recovery.
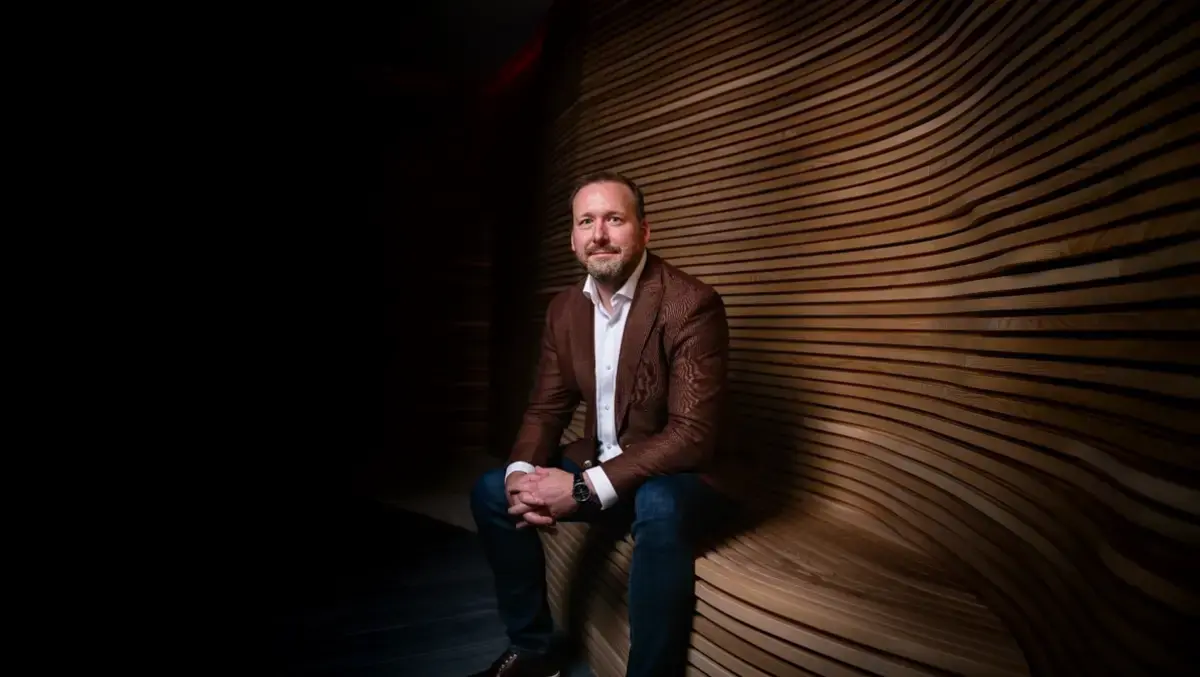
Mark Anderson, National Security Officer, Microsoft Australia & New Zealand, said the debate around AI and cyber risk had moved beyond theory.
"A year ago, much of the conversation about AI and cybersecurity was about what might happen. This year's data shows that what were theoretical risks last year have materialised into the reality we're navigating today. We're seeing AI embedded into malicious software, AI systems becoming targets in their own right, and the first real-world cases of attacks run largely by AI agents. Australia is part of that story," Anderson said.
The report describes AI as a tool now being used by both attackers and defenders. According to Microsoft, threat actors are applying AI to reconnaissance, social engineering, malware and exploit development, and to activity after an initial compromise.
At the same time, AI systems themselves are emerging as targets. Agents that can interact with enterprise data, applications, APIs and internal tools create additional security questions around identity, access, authentication, attribution and revoking permissions.
Identity focus
A recurring theme in the report is identity as a weak point. People, accounts, trusted access and exposed systems continue to feature prominently in the activity Microsoft tracks, even as AI changes the pace of operations.
Microsoft argued that standard security disciplines still apply to newer AI-linked systems. These include identity and authorisation controls, data protection, least privilege, monitoring, testing and secure software development.
Another area under scrutiny is vulnerability discovery. AI-assisted code analysis is making it easier to inspect software and identify weaknesses earlier, which may help defenders close gaps more quickly. But the same advances could also help attackers find flaws and build exploits faster.
Shared intelligence
Beyond technical controls, the report points to the value of combining information from across environments. Signals from endpoints, identities, cloud systems, applications, email, networks and threat intelligence become more useful when reviewed together, because activity spread across several systems may not be visible from any single source.
The same logic applies beyond one organisation, with information sharing between industry and government helping to connect indicators that would otherwise remain isolated. The report also notes that AI can help automate repeatable tasks, including pulling together relevant information so human analysts can focus on investigation and judgement.
Anderson set out three priorities for Australia in response to the findings.
"For Australia, that means getting three things right. First, make phishing-resistant authentication the norm, including greater adoption of passkeys. Second, bring AI into defence so security teams can detect, investigate and respond at machine speed. And finally, build genuine two-way information sharing between government and industry," Anderson said.
He added that no single entity has a complete view of the threat environment.
"No single organisation sees the whole picture. Our resilience as a nation will depend on how effectively we connect what each of us can see," Anderson said.