

Filigran: Does your CISO know enough?
Mon, 21st Sep 2026 (Today)
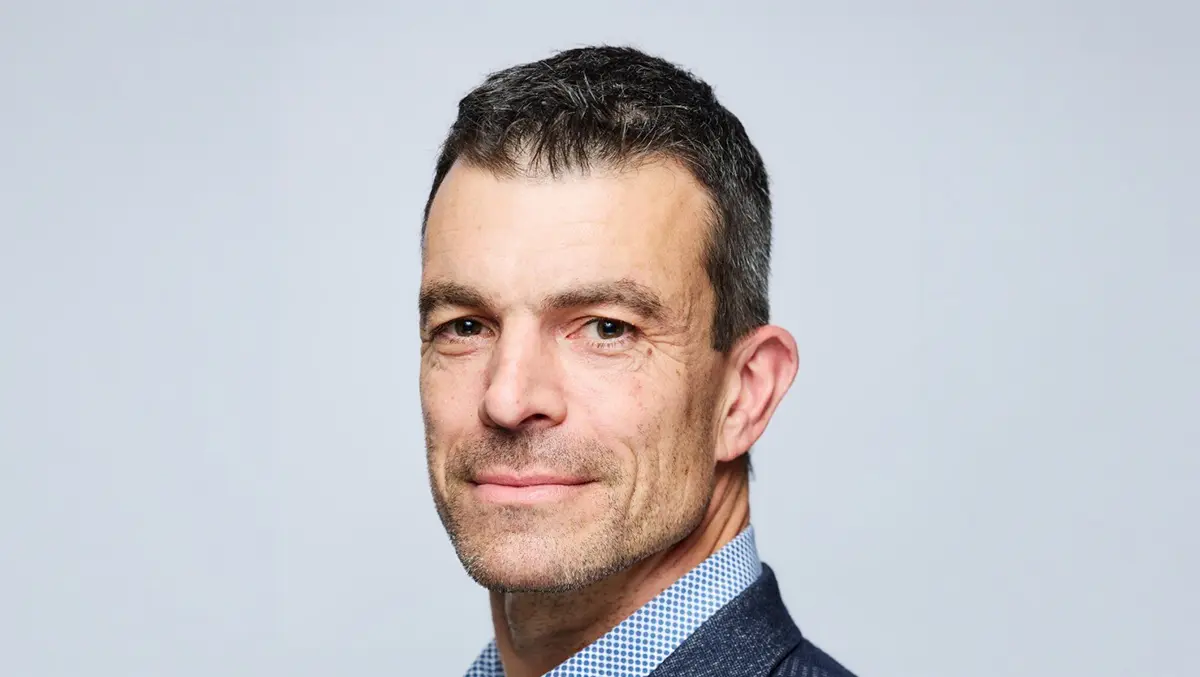
When a chief executive reads about a supply-chain attack over breakfast and asks whether the organisation is exposed, most security leaders still cannot answer on the spot. That gap, according to Damian Skeeles of Filigran, is why continuous threat exposure management (CTEM) is moving into the executive agenda.
Skeeles, who leads solution engineering for Filigran in Asia-Pacific and Japan, said the question is no longer whether organisations collect threat information. Almost everyone does, even if they do not call it that. "Anyone reading an article or a blog about an attack is consuming threat intelligence," he said. "We all do it, whether we know it or not."
Instead, it's all about what happens next. Intelligence that lives in a practitioner's head, a notepad, or a disconnected tool stack does not help a CISO when the board wants a binary answer: are we affected? And then, do existing controls stop it?
"The ideal state is that whenever you encounter a new threat, you should immediately understand if it has any relevance for your organisation, and have those answers at the ready," Skeeles said.
It isn't paranoia if they really are out to get you on the one hand. On the other, no need to worry about the irrelevant. The trick, of course, is discernment.
From knowing the threat to proving the defence
Filigran is a French cybersecurity company founded in 2022 on the back of two open-source platforms aimed at that loop. OpenCTI, short for Open Cyber Threat Intelligence, structures the work security teams already do informally: identifying who is attacking, who might attack, and what that means for the organisation. OpenAEV, or Open Adversarial Exposure Validation, tests the follow-up question: with the threat and actor identified, can the attacker actually get in?
Skeeles described the pair as complementary rather than overlapping. OpenCTI formalises intelligence that would otherwise remain unstructured. OpenAEV then asks whether current security architecture, configurations and controls would hold if that threat were aimed at the organisation.
On the back of the base created by these products aimed at CTEM, and appreciating the gap between identifying issues and taking meaningful action (starting with ready access to those key binary questions) Filigran recently-introduced XTM One.
Through an AI-native orchestration layer, the platform unifies OpenCTI and OpenAEV into a single CTEM workflow, alongside autonomous penetration testing. This, said Skeeles, alleviates manual operational bottlenecks and tool-switching with dedicated AI agents handling threat data and scenario generation. The result, then, is that threat intelligence is backed by action and the ability to confidently and rapidly answer questions around adequate protection.
"Urgency around questions of vulnerability and protection is growing because of geopolitics, generative AI and a shift away from treating vulnerability management as a patching exercise," he added. "Now, prioritisation and exposure management focuses on mitigating actual threats rather than a broad 'worry about everything' approach."
While its clients are concentrated in governments and large banks, Skeeles said Filigran is seeing more mid-size enterprises with full-time security staff, but not dedicated threat-intelligence specialists, looking for ways to rank vulnerabilities and understand relevant threats as an essential part of their protection regimes.
The 'open' advantage: flexibility, responsiveness
Open source tools like those from Filigran offer advantages which are becoming more pronounced in the AI age. Asked what those advantages are, specifically, Skeeles contextualised the question in terms of threat intelligence. "There's a lot of adoption and intelligence work in government agencies. In the regions we cover, a closed source tool doesn't necessarily provide visibility into what the tool itself is doing - and there are sizable risks with that, which can also slow down the response."
By contrast, said Skeeles, open source allows expanded due diligence: when the technology can be interrogated and dissected to the nth degree, confidence follows where confidence is most required. "Practitioners want to understand the tools they're using. They may also want to modify the tools. Especially with agentic AI, practitioners are customising their tools and processes, and want tools they can get their teeth into where, if they don't like something, they can change it."
He said this is emerging clearly from within the APJ region. "When meeting with customers, I'll bump into enthusiasts who say they're doing these really cool things for particular use cases. They use that flexibility to start from a base and change to the way they want to work and that's an advantage for them, and an advantage for us."
Ultimately, though, Skeeles said it boils down to accurate, timely, and relevant information. That's the crux of threat intelligence.
Hope is not a strategy
Asked what 'good enough' cybersecurity looks like in 2026, Skeeles said it is always a moving target where even the right combinations of technology, people and practice are no guarantee. "Sometimes, you'll get lucky even if your protections are inadequate. Other times, you'll get unlucky with entirely suitable security solutions," he noted.
What he does as consistent factors for success includes security teams who engage the business, find internal champions, and build a culture that treats cyber risk with the same seriousness as health and safety. And he said the market itself has generally improved in response to broader risk awareness. "Security is no longer confined to the basement. CISOs are being elevated to the board, and boards more often treat cyber risk as an executive issue."
Hope of avoiding compromise, Skeeles agreed, is not a strategy. "At the end of the day when you're planning your security architecture and you're trying to fit the pieces together and reviewing how everything works you need to understand if it actually works when it matters most. And the proof of the pudding is in the eating; when there's any new threat or major headline, even if it hasn't yet affected your organisation, can you answer with certainty, right now, if it will affect you?"