
Getac urges layered security for rugged devices in defence
Thu, 29th Oct 2026 (Today)
Getac has urged Australian defence and frontline organisations to take a layered approach to securing rugged computing devices, arguing that security depends on design, configuration and ongoing management, not just individual features.
The comments come as organisations face tighter scrutiny of equipment configurations, physical protection and lifecycle controls for frontline technology. Getac argued that authentication and endpoint protection alone do not address risks tied to hardware interfaces, connected equipment and device customisation.
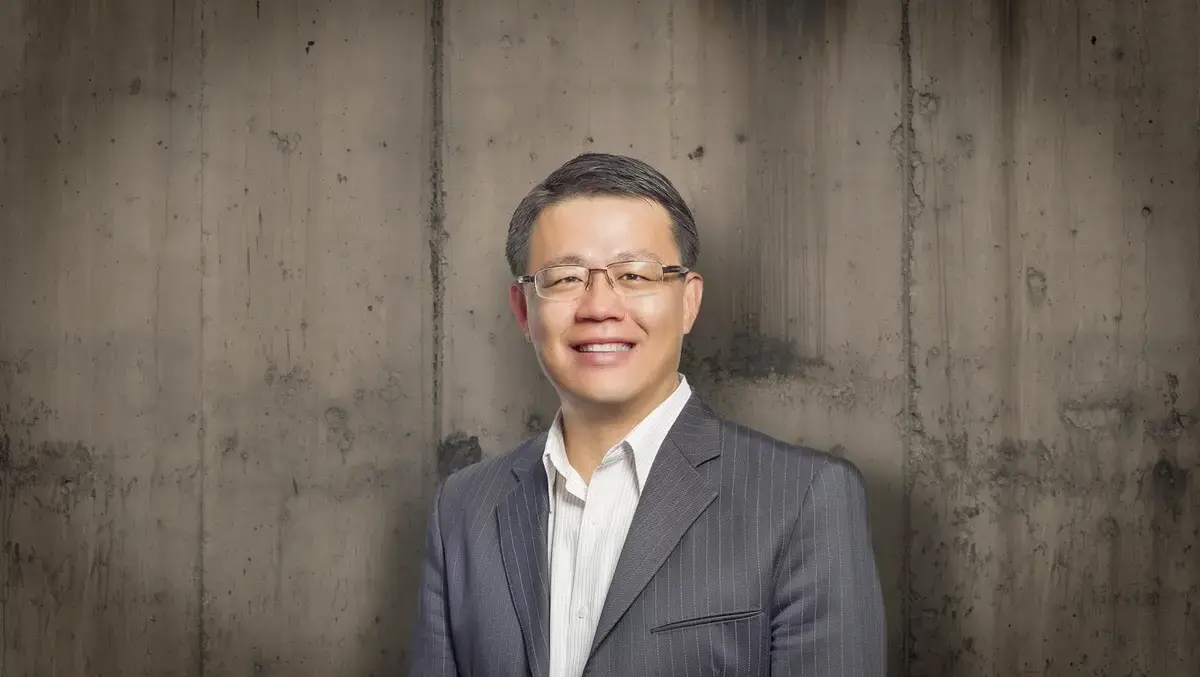
Jerry Huang, Vice President, Global Market Development, Getac, said, "One of the challenges with frontline security is that the controls needed to protect information can also restrict how personnel work. Disabling a port or wireless connection may reduce exposure, but it could also prevent access to essential equipment or communications. The manufacturer's role is to help resolve those trade-offs at the design and configuration stage, so security requirements don't become operational constraints in the field."
Use case first
Security planning should begin with how a device will be used in practice. In frontline environments, rugged computers may be shared between users, moved across locations or left unattended, creating risks that basic access controls do not fully address.
Encryption is one part of that picture, particularly where devices hold sensitive operational data. Getac pointed to removable solid-state drives as one way to separate data from hardware, but said organisations still need procedures for encryption, storage, media handling and any information retained elsewhere on the device.
Attention is also shifting lower down the technology stack. Firmware-level attacks can compromise systems during startup, potentially bypassing controls that operate within the operating system. Hardware-backed root-of-trust technologies, including Trusted Platform Module 2.0 processors and Microsoft Secured-core PC architecture, can help establish a trusted base for system integrity and protect encryption keys, according to Getac.
That creates a procurement issue for defence buyers because software protections may not be enough if the underlying platform cannot support the required security architecture. Organisations therefore need to test whether a rugged device can meet operational and information-handling requirements at the same time.
Beyond the device
Getac also highlighted risks created by interfaces and peripherals. Wireless modules, cameras, microphones and external ports may be necessary in one deployment but restricted in another. The same issue extends to docks, communications equipment and specialist peripherals connected to rugged computers.
In practice, a device can appear secure in isolation while introducing risks once it becomes part of a wider operational system. Australian organisations should examine whether manufacturers can support the required configuration across the full deployment, rather than on the core unit alone, Getac said.
Physical access
Physical security remains separate from device durability, according to Getac. Frontline equipment is often transported between sites, installed in vehicles or used in settings where staff cannot supervise it continuously, exposing systems to tampering and unauthorised access.
Measures such as physical locks, controlled storage and restrictions on internal components can reduce some of that exposure. For more sensitive environments, Getac cited customised rugged laptops with chassis intrusion detection that remains active when a device is powered off and can trigger a motherboard lockout if tampering is detected.
Huang said, "Durability and information security should not be treated as equivalent. A device designed to withstand physical impacts or environmental exposure still requires appropriate controls against unauthorised access and interference."
Lifecycle checks
Security can weaken after deployment if organisations do not maintain approved configurations during repairs, updates and redeployments. Devices may change roles, receive firmware updates or be replaced while the wider system remains in service, and each of those changes can alter the original security posture.
Data handling at end of use is another concern. Getac said deleting files or restoring factory settings does not necessarily make information unrecoverable, so defence organisations should consider physical data separation and sanitisation methods when equipment is transferred, serviced or retired.
The same principle applies to repaired or replacement units. If a rugged computer was originally configured to restrict interfaces or support specialist controls, the replacement should be checked against the same approved settings before it returns to service.
Huang said, "It is important to establish how approved settings will be documented, how replacement equipment will be configured, and whether specialist requirements can continue to be supported as technology changes. A secure configuration at the point of purchase has limited long-term value if it cannot be maintained throughout the device's working life."
Getac's broader argument is that frontline security should be treated as an architecture rather than a single certification or product feature. Procurement teams need to assess hardware, connected equipment, data handling and long-term support together when choosing rugged computing systems for sensitive environments, it said.