

TrendAI launches autonomous vulnerability discovery on AWS
Fri, 2nd Oct 2026 (Today)
TrendAI has launched a private preview of TrendAI Vision One Autonomous Vulnerability Discovery for enterprise customers running on AWS in Australia and New Zealand.
The product is designed to identify vulnerabilities in customer source code, including zero-day flaws, and verify fixes after patches are deployed. It operates within a customer's AWS environment and uses TrendAI's AESIR exploit-remediation engine alongside input from the company's Zero Day Initiative research team.
The launch comes as security vendors respond to a rise in AI-assisted software development and the prospect of attackers finding vulnerabilities faster. TrendAI is positioning the service as a way for organisations to inspect code inside their existing development environments rather than move repositories to a separate system.
The service runs on Amazon Bedrock and is built around a multi-model AI architecture that mainly uses Anthropic models. Customers continue to use their existing code repositories and version control systems, while scans and patch verification remain inside their AWS environment.
Under the process described by TrendAI, the service begins with a scoping interview to assess a customer's environment. A Zero Day Initiative expert then defines and tunes a custom scan, after which the service team monitors and controls each scan rather than leaving the process fully unsupervised.
Once a scan is complete, customers receive a vulnerability report with a severity rating, an estimated CVSS score, and a detailed write-up for each finding. After a customer deploys a patch, the scan is repeated to confirm that the issue has been fixed.
Validation Layer
A central element of the offering is TrendAI's Zero Day Initiative, which it describes as the world's largest vendor-agnostic bug bounty programme. Findings from the AI system are checked against more than two decades of research from the programme and reviewed by its experts, including those associated with the Pwn2Own hacking competition.
This validation layer is intended to reduce false positives, a long-running problem in automated vulnerability scanning and static analysis. TrendAI also said internal benchmarking showed its AI models identified more true-positive vulnerabilities with fewer false positives than leading scanning and static analysis tools, though it did not disclose comparative figures.
The company also pointed to an evaluation on the CyberGym testing framework, where the AESIR engine outperformed single-model and other agentic system scores on the CyberGym leaderboard. TrendAI is using that benchmark result to support its case for agentic AI in vulnerability discovery and remediation workflows.
AWS Focus
The release is initially limited to selected enterprise customers on AWS, with pricing tailored to the scope of scans and the deployment model. TrendAI's emphasis on native deployment in Amazon Bedrock reflects a broader market shift towards keeping security tools close to where code is stored and where cloud workloads already run.
For customers, that may help address concerns about control of source code and the use of external AI tools. TrendAI said source code stays within the customer's AWS environment, while existing Git repositories and code registries remain the system of record.
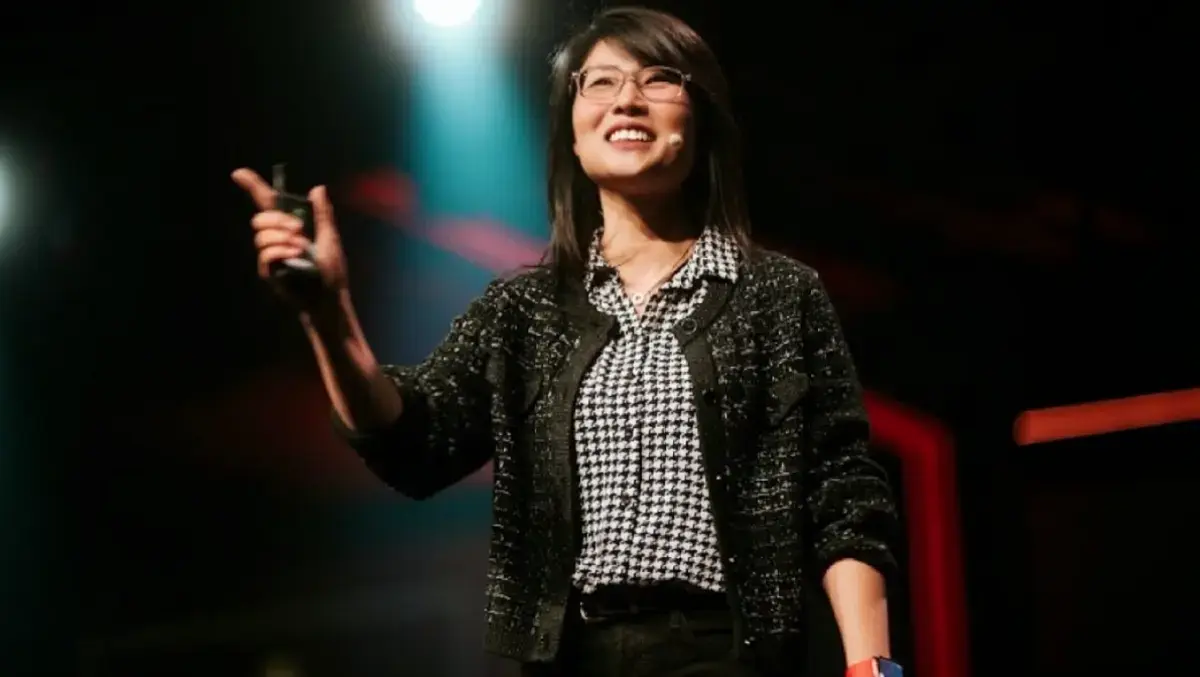
Rachel Jin, Chief Platform and Business Officer and Head of TrendAI, said the pace of software development and attackers' use of AI were reshaping vulnerability discovery. "AI is changing both sides of vulnerability discovery. Code is being written faster than ever, and attackers are using AI to find flaws faster than ever," Jin said.
She said the company was trying to combine machine-led analysis with human review from specialist researchers. "Security teams shouldn't have to choose between the speed of AI and the judgment of the world's best vulnerability researchers. Autonomous Vulnerability Discovery puts AI built for accuracy together with two decades of ZDI research, and runs it where customers' code already lives, so they can find and fix what matters before attackers do," she said.