

BeyondTrust links privilege data to CrowdStrike Falcon
Thu, 24th Sep 2026 (Today)
BeyondTrust has introduced new integrations between its Pathfinder Platform and CrowdStrike Falcon Next-Gen SIEM, bringing BeyondTrust identity and privilege data into the Falcon platform.
The integrations are designed to give joint customers a single view of privilege risk and threat activity by combining identity relationships and privilege exposure data with Falcon security telemetry.
Security teams face growing pressure to detect attacks that rely on compromised credentials rather than malware. BeyondTrust's Phantom Labs research found that about 75% of modern attack paths exploit identity relationships rather than software vulnerabilities alone.
The new integrations cover several Pathfinder Platform products, including Endpoint Privilege Management, Password Safe and Privileged Remote Access.
Endpoint Privilege Management sends policy changes, privilege elevation requests and blocked execution events into Falcon. Password Safe adds privileged access information to the Falcon console, while Privileged Remote Access shares configuration changes, console authentications and session activity tied to cloud and network infrastructure.
Identity focus
The announcement reflects a wider shift in cybersecurity towards identity and privilege as central indicators of risk. As organisations manage a growing mix of human users, service accounts and AI agents, security teams are under pressure to understand how those identities relate to access rights and potential attack paths.
The integrations are intended to close the gap between prevention and detection by adding identity context to incident investigation. In practice, analysts using Falcon can see not only threat signals but also the privileges and relationships attached to the identities involved.
That visibility matters because attackers often move through an organisation by abusing legitimate access. Correlating telemetry with privilege exposure can help security teams determine whether an alert is tied to a highly privileged account, a remote session or a recent policy change.
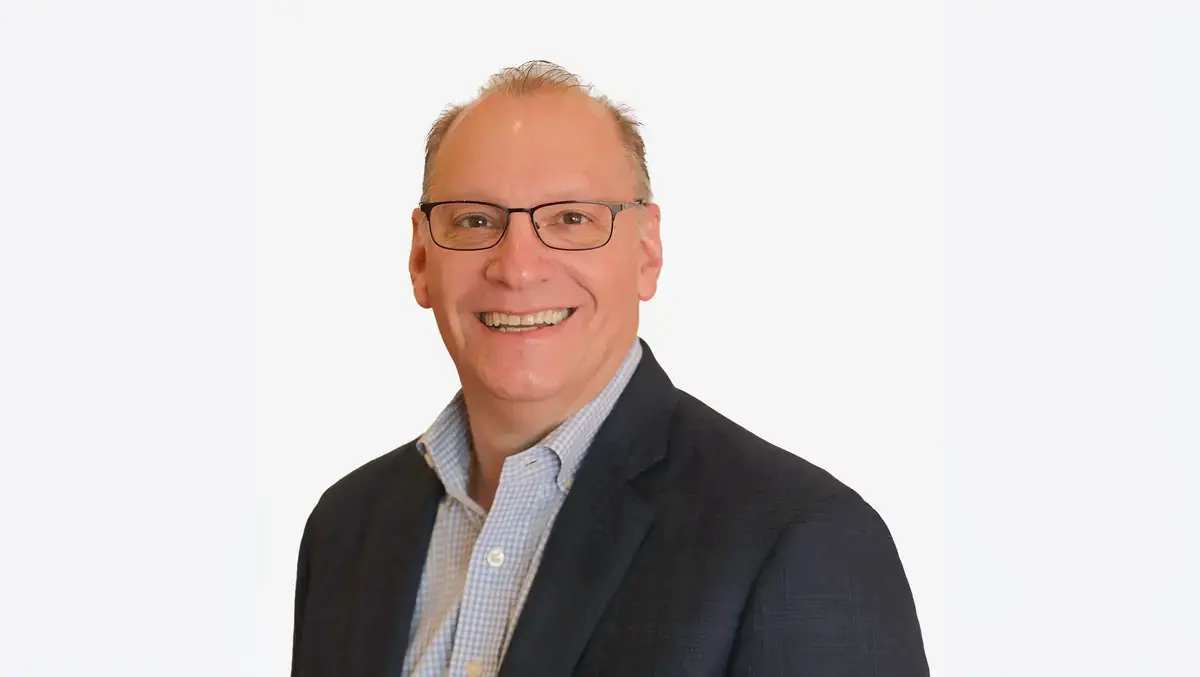
David Manks, Vice President of Strategic Alliances at BeyondTrust, commented on the trend behind the launch.
"Attackers increasingly exploit legitimate identities and privileges to move through enterprise environments, making identity context critical to understanding and responding to threats," said David Manks, Vice President of Strategic Alliances at BeyondTrust. "By bringing BeyondTrust's identity and privilege intelligence into CrowdStrike Falcon, joint customers can connect privilege risk with threat activity, bringing identity threat prevention and detection together to accelerate investigation and response."
Broader platform
The integrations also extend BeyondTrust's Pathfinder strategy, which centres on identifying, prioritising and reducing privilege risk across different classes of identity. The company has increasingly emphasised non-human and AI-linked identities as more software agents and automated processes gain access to systems and data.
For buyers, the launch points to continued consolidation across cybersecurity tools, as vendors seek to feed more specialised data into broader detection and response platforms. SIEM products have become a focal point for that effort because they serve as central hubs for alerting, investigation and response workflows.
BeyondTrust says its customer base includes more than 20,000 organisations, including 75 of the Fortune 100. The company positions privilege as the key risk factor in identity security, arguing that the issue is not simply who or what an identity is, but what access it holds.
The CrowdStrike integration gives customers another way to use that data within an existing security operations environment. It also underlines the commercial importance of partnerships between specialist identity security providers and larger platform vendors that already sit at the centre of many enterprise security teams.