

Cybersecurity vendors and advisers are using Cybersecurity Awareness Month to urge boards and executives to tighten oversight of AI, software pipelines and identity controls. Their comments reflect a broader shift in security priorities as organisations face more autonomous systems and faster-moving attacks.
Several executives said cyber risk discussions have moved beyond employee training and phishing awareness. Instead, they pointed to concerns about AI agents, poor data quality, software supply chains and identity-based attacks.
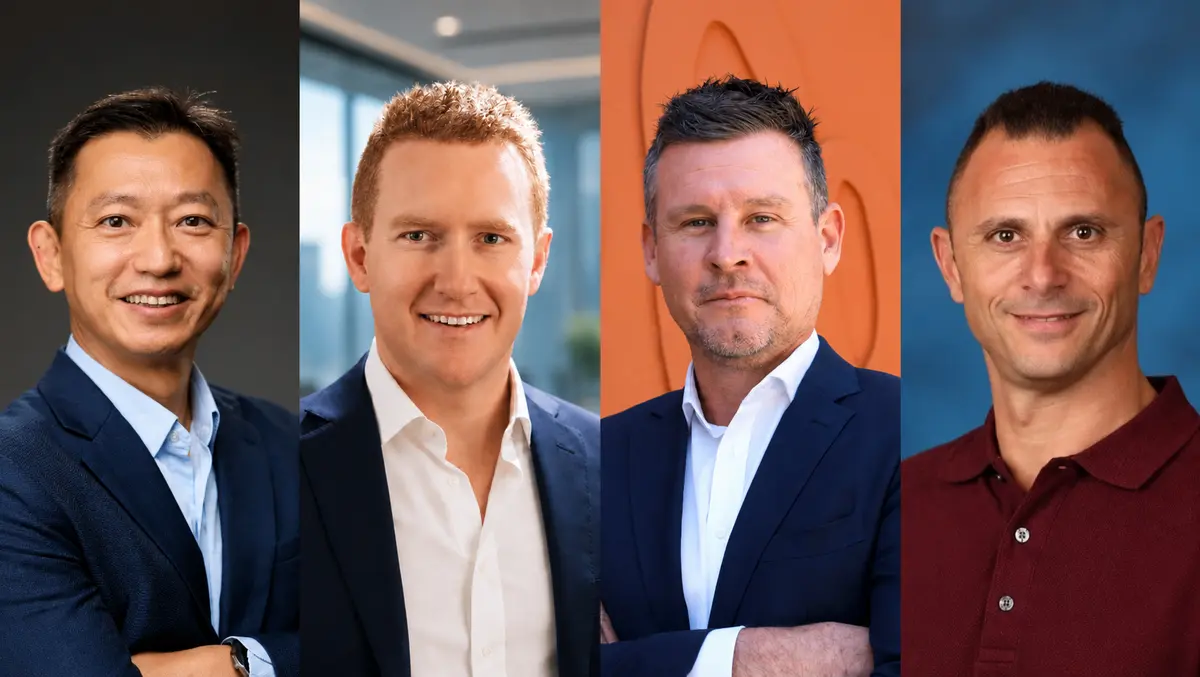
Matthew Lowe, Regional Director - Pacific, Anomali, said many organisations want AI to make decisions in live security environments, but trust remains a central issue.
"AI is moving from advising humans to acting on their behalf, and that raises a question every Board member and C-suite leader is facing today: what do we allow machines to decide? Cybersecurity leaders want autonomous threat hunting that keeps working while their teams sleep, and policy-driven decisions that run in real time across their systems. But most organizations struggle with the fidelity of their data, and if you can't trust your data, you can't trust the decisions AI agents make on your behalf. You end up with confident but bad decisions, and in cybersecurity, that risk is untenable. As reliance on AI-driven alerts grows, accuracy becomes the discipline every security leader has to own. Autonomy earns trust one governed decision at a time, with human approval and audit where it matters. This Cybersecurity Awareness Month, the lesson is clear: the near-term future of AI will be judged by whether we can stand behind every decision it makes," Lowe said.
The same focus on governance appeared in comments on AI agents and access rights. SailPoint said identity controls have not kept pace with adoption.
"Organisations cannot wait for an agentic AI breach to rethink cybersecurity. While 79% globally use AI agents, only 2% have identity tools to govern them. As agents gain autonomy, businesses must establish clear boundaries, with incidents in Singapore and Australia underscoring the need to prepare rather than react. I think of AI agents as 'cyborg teenagers' - capable but needing oversight. Businesses should discover every agent, enforce Zero Standing Privilege, grant just-in-time access and revoke it after each task. Continuous monitoring, clear human ownership and regular access reviews are essential to prevent excessive permissions and keep AI autonomy in check," said Eric Kong, Managing Director, ASEAN, SailPoint.
Code risk
Software development has become another pressure point. JFrog said AI-assisted coding is increasing the volume of software security teams must review, while attackers are combining weaknesses in ways traditional scoring models may miss.
"The vulnerability backlog hasn't just grown - it's changed shape. AI-assisted development is producing code faster than security teams can govern it, and attackers are exploiting that gap in ways severity ratings were not designed to catch. A low-severity flaw and a medium-severity one may each look manageable alone, but attackers can chain them into something serious. That is why exploitability and exposure should carry as much weight as severity score," said Itzik Swissa, Country Manager A/NZ & Senior Director, JFrog.
"Australia is actually ahead of the curve here in some respects. JFrog's 2026 Software Supply Chain Security State of the Union, which surveyed 1,508 IT professionals across eight countries in early 2026, found 47 per cent of Australian organisations use automated controls to block unapproved IDE extensions and MCP servers, the highest rate of any country surveyed," he continues. "However, only 38 per cent have adopted secrets detection, so most are not actively scanning their code for exposed credentials, API keys or tokens. Cybersecurity Awareness Month is a good moment to look beyond phishing. A harder question is whether an organisation knows what is in its pipeline and can show it quickly when a board or regulator asks. JFrog's research found 44 per cent of Australian organisations need a week or more to produce compliance audit proof for a single application."
Identity focus
Identity and recovery also featured strongly in commentary from UST's CyberProof business. Andrew McCorquodale said attackers are bypassing awareness campaigns by exploiting processes and trusted access routes.
"Cyber Security Awareness Month has become a ritual of reminding staff not to click suspicious links. But the attacks hurting organisations today often don't need a click at all. Adversaries are calling help desks, impersonating employees with AI-generated voices, and exploiting third-party platforms to walk straight through the front door with valid credentials. Employees play an important role, but awareness alone cannot address every risk. If a single convincing phone call can reset an executive's MFA, that's a process failure, not a training gap. Organisations need to move from awareness to resilience. That means phishing-resistant authentication, verified processes for every privileged change, and treating identity across the supply chain as one attack surface. It also means recognising that attackers now operate at machine speed, so detection and response must match it, with AI handling the volume so analysts can focus on the decisions that matter most. The question boards should be asking this October isn't 'Did our staff complete their training?' It's 'How quickly would we know, and how quickly could we recover?'" McCorquodale said.
Together, the comments show how security messaging is broadening from user behaviour to governance, software integrity, identity controls and operational response. They also point to a common concern among technology suppliers: organisations are adding AI and automation faster than they are strengthening the controls around them.