
DigiCert adds Secure Releases to Software Trust Manager
Fri, 23rd Oct 2026 (Today)
DigiCert has added Secure Releases to its Software Trust Manager. The feature links release information with vulnerability data and software bills of materials.
It is intended to help organisations track software risk both at the time of release and later, when new vulnerabilities are identified.
Secure Releases combines data from supported GitHub releases with software bills of materials, known vulnerabilities, severity ratings and security scan results. It is designed to help teams identify which software versions are affected by a vulnerable component and use that information in signing and release workflows.
The feature is aimed at a gap that can emerge after software has shipped. Software signing can verify the source of code and show whether it has been changed, but it cannot show whether a component later becomes vulnerable.
Security teams often need to cross-check repositories, bills of materials, vulnerability databases and scanner outputs to determine which releases are exposed. Secure Releases brings those records together at the release level so teams can see which versions need attention.
Risk tracking
Software Trust Manager users can sign software and cryptographic inventories, including software bills of materials and cryptographic bills of materials. Recipients can then verify the source and integrity of those records.
The new functionality also lets teams view dependencies, associated bills of materials, vulnerabilities, severity ratings and supported scan findings for each release. Users can monitor releases as vulnerability information changes over time, helping them spot new risks tied to previously shipped software.
Another part of the feature is intended to help teams find releases that contain a vulnerable component and notify the groups responsible for them. Premium-tier users can also identify a newer version of a component if a fix is available.
Organisations can set vulnerability and software bill of materials requirements within release policies. Where supported, those policies can be used to stop signing or release when the requirements are not met.
The system can also be used to sign related security evidence, including security evaluations, VEX statements, SLSA attestations and SARIF reports for customers and auditors.
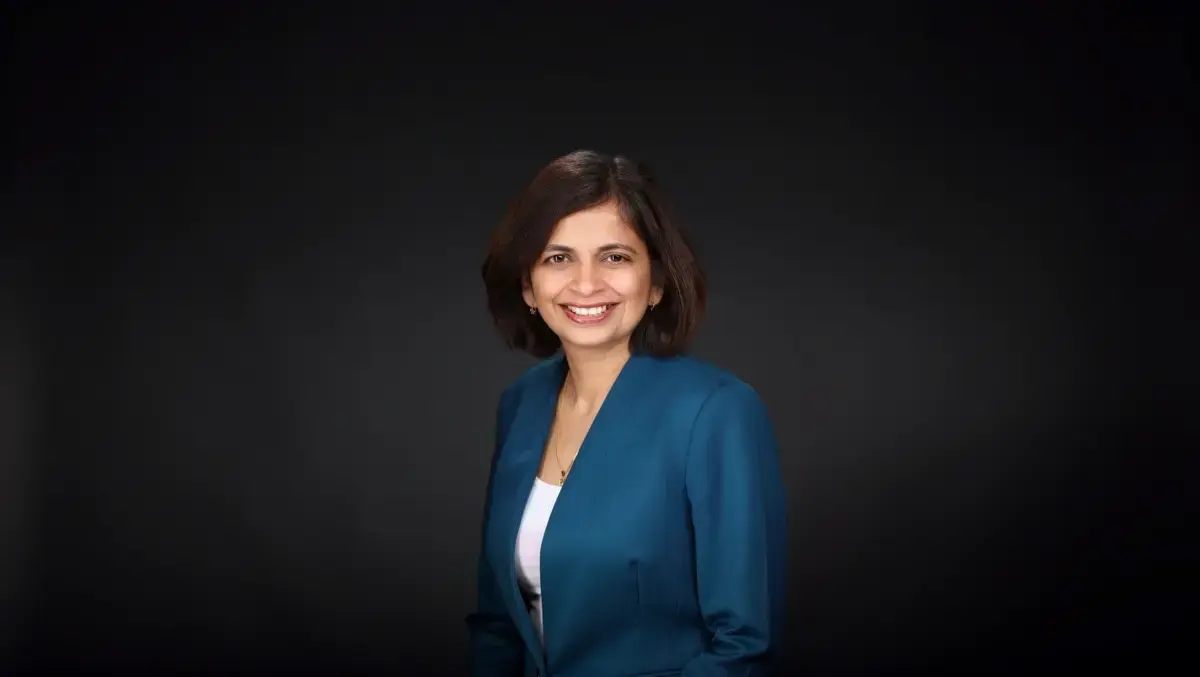
Deepika Chauhan, Chief Product Officer at DigiCert, said the new feature ties release monitoring to existing signing controls.
"Software signing proves where code came from and whether it has been altered, but those assurances do not tell teams whether a release contains a newly discovered vulnerability dependency," said Deepika Chauhan, Chief Product Officer at DigiCert.
"Secure Releases brings those pieces together. By connecting release risk to the same policies that govern signing and delivery, organisations can respond faster when exposure changes and keep software from moving forward when it does not meet their requirements."
Product tiers
Secure Releases is available through the Essentials, Advanced and Premium editions of Software Trust Manager. Essentials offers a point-in-time assessment of release risk, while Advanced and Premium add ongoing monitoring of software bill of materials results by release as vulnerability data changes.
Premium adds two further controls. It can suggest a newer version of a vulnerable component when a fix exists, and it can allow organisations to block signing or release if software does not meet their security requirements.
DigiCert describes Software Trust Manager as part of its DigiCert ONE platform. It says it works with more than 125,000 organisations, including 90% of the Fortune 500.