
DigiCert wins ISO 27001 certification for security systems
Wed, 28th Oct 2026 (Today)
DigiCert has achieved ISO/IEC 27001:2022 certification for the information security management system that supports its global Certification Authority and Trust Services operations. The certification covers operations in 11 countries and a globally distributed remote workforce.
It applies to the issuance and management of publicly and privately trusted digital certificates, the Public Key Infrastructure processes that support them, and a range of corporate functions linked to those services. The certification followed an independent audit by MSECB against the ISO/IEC 27001:2022 information security management standard.
The assessment reviewed security policies, processes and controls across operations in the United States, United Kingdom, Ireland, the Netherlands, Belgium, Germany, Switzerland, Latvia, Australia, India and South Africa.
Audit scope
In scope are Governance, Corporate IT Operations, PKI Operations, Authentication & Support, Engineering, Security, Compliance, Risk, Legal, Product and Human Resources, where those functions support the covered services.
The information security management system covers information security governance and risk management, identity and access controls, data protection and encryption, secure product development and change management, supplier and third-party risk management, vulnerability management and incident response, continuity and recovery readiness, employee security awareness and training, and security monitoring and performance evaluation.
DigiCert said the certification is intended to give customers and partners independent validation of its approach to information security. It added that the standard may support vendor risk assessments and procurement reviews, particularly for customers in regulated sectors and public bodies.
The certification adds to a broader set of external assessments held by the business. DigiCert also maintains SOC 2 Type II, WebTrust for Certification Authorities, WebTrust Baseline Requirements, WebTrust Extended Validation and Code Signing, and European Telecommunications Standards Institute standards for qualified trust services.
Security focus
ISO/IEC 27001:2022 certification requires ongoing surveillance audits and periodic recertification rather than a single review. The process is designed to test whether the information security management system continues to operate effectively as technology, threats and regulatory requirements change.
DigiCert provides digital certificates and related trust services used to verify identities, secure communications and support Public Key Infrastructure environments. Its certified scope includes both publicly trusted and privately trusted certificate operations.
According to DigiCert, its customer base includes more than 125,000 organisations, including 90% of the Fortune 500. The company describes its platform as combining PKI, DNS and certificate lifecycle management across infrastructure, software, devices, messages and AI-related content and systems.
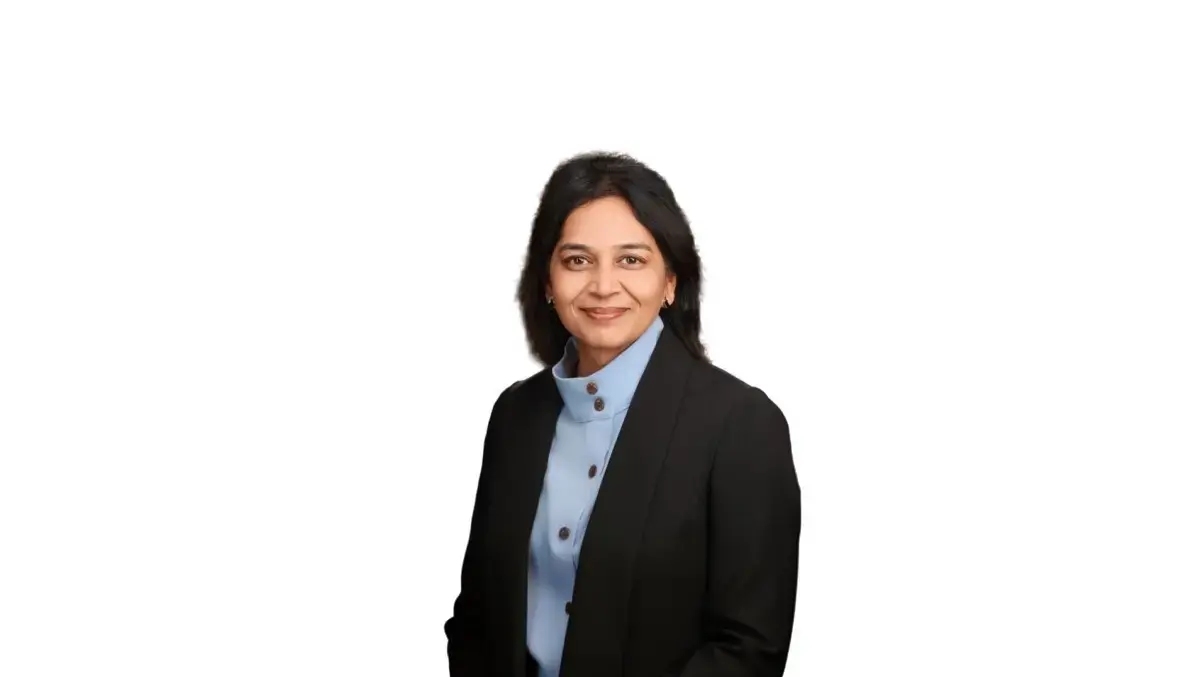
One executive said the certification was intended to give external parties more confidence in how the company manages security and risk across its operations.
"Trust is strongest when it can be independently verified," said Lakshmi Hanspal, Chief Trust Officer at DigiCert. "ISO 27001 certification gives our customers and partners additional assurance that the same disciplined approach to security and risk management that underpins our solutions also governs how we protect information and operate our business. As cloud environments, machine identities and AI systems expand, organisations need technology providers that can demonstrate and assert that security and continuous improvement are built into their operations."