
Kapālins names Jai A Singla CTO as it tightens AI controls
Fri, 30th Oct 2026 (Today)
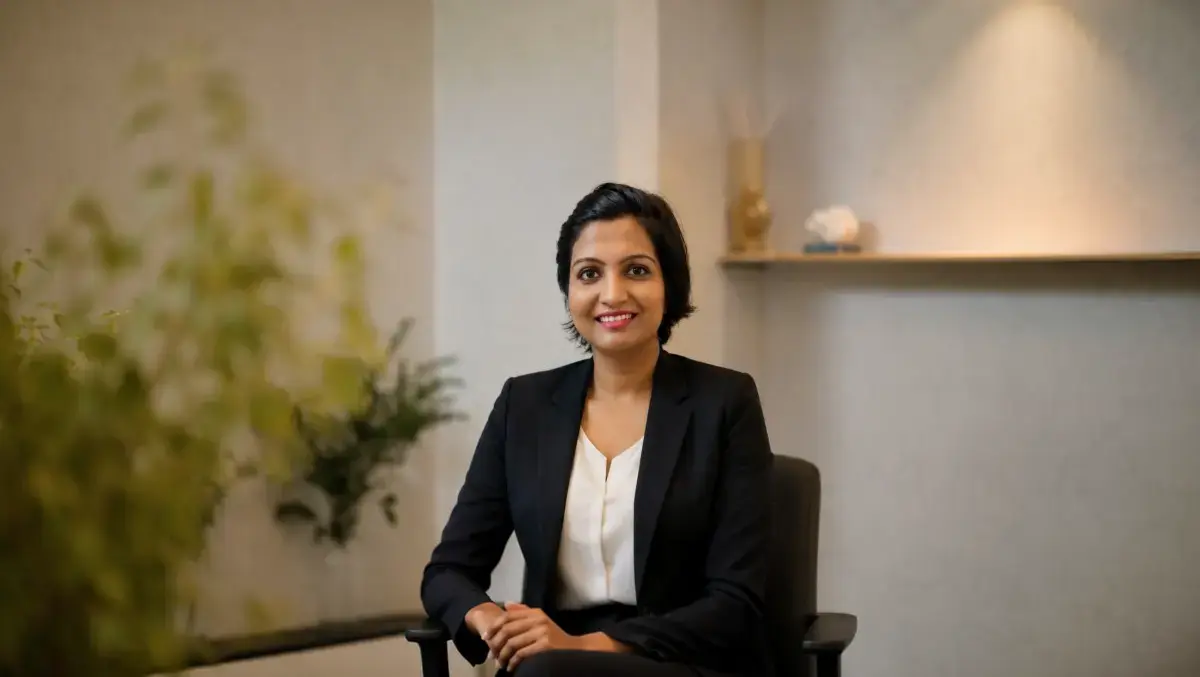
Kapālins has appointed Jai A Singla as Chief Technology Officer and a director as the Australian AI security company expands its focus on controls for autonomous AI systems.
Singla joins the leadership team with more than 20 years of experience across networks, security and identity. His background covers identity and access management, privileged access, Zero Trust and AI security, with work spanning financial services, telecommunications and government.
He will oversee platform architecture, Kapālins Labs and its research, the security of agentic AI and non-human identities, and technical go-to-market work worldwide.
The appointment coincides with a product announcement tied to Anthropic's Claude Enterprise service. Kapālins has introduced what it calls guardrail integrity for Claude Enterprise, designed to block prompt-injection attempts, risky agent actions and sensitive data exposure before Claude executes a request.
Under the integration, governed prompts and tool calls from claude.ai, Cowork, Claude Code and Claude Tag are checked before they run. The same Policy Shield rules Kapālins applies across other AI systems are used here, including checks for prompt-injection and jailbreak attempts, limits on agent tool use, approved model settings and 57 sensitive-data patterns.
Kapālins also monitors whether those controls remain in place. By reading Claude Enterprise activity records every 15 minutes through the Compliance API, it raises a critical alert if an Inference hooks configuration is deleted or changed, if a request proceeds without a verdict, or if single sign-on, data residency or zero-data-retention settings are switched off or weakened.
In total, the system watches 30 kinds of risky change, according to Kapālins. It also flags higher-risk operational changes such as broader agent autonomy or the addition of a new MCP server.
AI oversight
The dual announcement reflects a wider shift in security thinking as AI systems move beyond question answering into more autonomous actions. Kapālins argues that the traditional security principles of confidentiality, integrity and availability now need to be applied directly to models and agents, not only to the infrastructure around them.
To support the case for closer oversight of agent behaviour, the company pointed to research from the UK AI Security Institute and METR. It cited findings on agents taking actions outside their brief and on a share of longer-task successes that were not legitimate.
Ritu Singla, Chief Executive Officer of Kapālins, linked the leadership change to that shift in operational risk.
"AI is starting to act for the organisations that run it, and the controls have to come first," said Ritu Singla, Chief Executive Officer of Kapālins.
"Jai has spent two decades building and securing systems inside large, regulated organisations. That is the experience this moment needs."
For Kapālins, the Claude Enterprise integration is also intended to provide audit evidence. Verdicts and activity logs can count as evidence towards 24 controls across 20 compliance frameworks, including APRA CPS 234, the NIST AI RMF, the EU AI Act, DORA, MAS technology risk guidelines, CBUAE AI guidance and Korea's AI Basic Act, according to the company.
That compliance angle may matter for banks, insurers and other regulated users trying to document how AI systems are governed. Kapālins says its broader framework map spans 42 frameworks across 15 jurisdictions.
Technical checks
The integration relies on Claude Enterprise Inference hooks, which Anthropic introduced in beta in August. Kapālins said it built its endpoint to the published Inference hooks contract, passed all 17 required checks and returned 95% of verdicts within 229 milliseconds in its own testing.
Organisations can configure whether prompts are blocked or allowed through if a decision is not returned in time, with a default response window of 2.5 seconds, the company said. If a prompt is denied, the user is shown the reason.
Kapālins also said verdicts store no prompt text and that content capture is off by default. The Compliance Access Key is read-only and encrypted with AES-256-GCM, it said.
Singla said the product announcement fits directly with the security problem he has been hired to address.
"Confidentiality, integrity and availability have anchored security for decades. What has changed is that the systems we protect have started to act for themselves," said Jai A Singla, Chief Technology Officer of Kapālins.
"Models get more capable with every release and will soon act faster than anyone can review. An agent that remembers can be taught the wrong thing and keep acting on it for as long as nobody checks. My job is to make sure every model and agent an organisation runs stays confidential, intact and available, and that someone keeps checking how it behaves."