
Keeper Security has launched an AI-based phishing protection feature for its browser extension, designed to warn users before they enter credentials on fraudulent login pages.
The feature is available as an opt-in setting in version 18.2.0 of the Keeper Browser Extension.
It uses an on-device AI engine to identify signs commonly associated with phishing sites, including look-alike domains, spoofed websites and pages that imitate known brands. Website analysis is performed locally in the browser rather than sending user data elsewhere.
Keeper said the feature targets a common cyber security attack in which users are persuaded to enter passwords into fake login pages that closely resemble legitimate services. It cited the 2026 Verizon Data Breach Investigations Report, which found credential abuse was involved in nearly 40% of breaches.
How it works
The local AI engine evaluates web pages for structural patterns commonly linked to credential harvesting. These include domain impersonation through typosquatting, login details hidden in URLs, suspicious IP addresses, unusual link structures and sites requesting password inputs from unofficial or untrusted domains.
If a site is flagged, users receive a warning that identifies the threat pattern. They can then block the site, dismiss the warning or disable Keeper on that site. Users retain control of their blocked sites list and can restore access at any time, while administrators can also re-enable access and autofill through the Keeper Admin Console.
The product is disabled by default. Individual users can configure it through the browser extension, while IT teams can enable and manage it centrally.
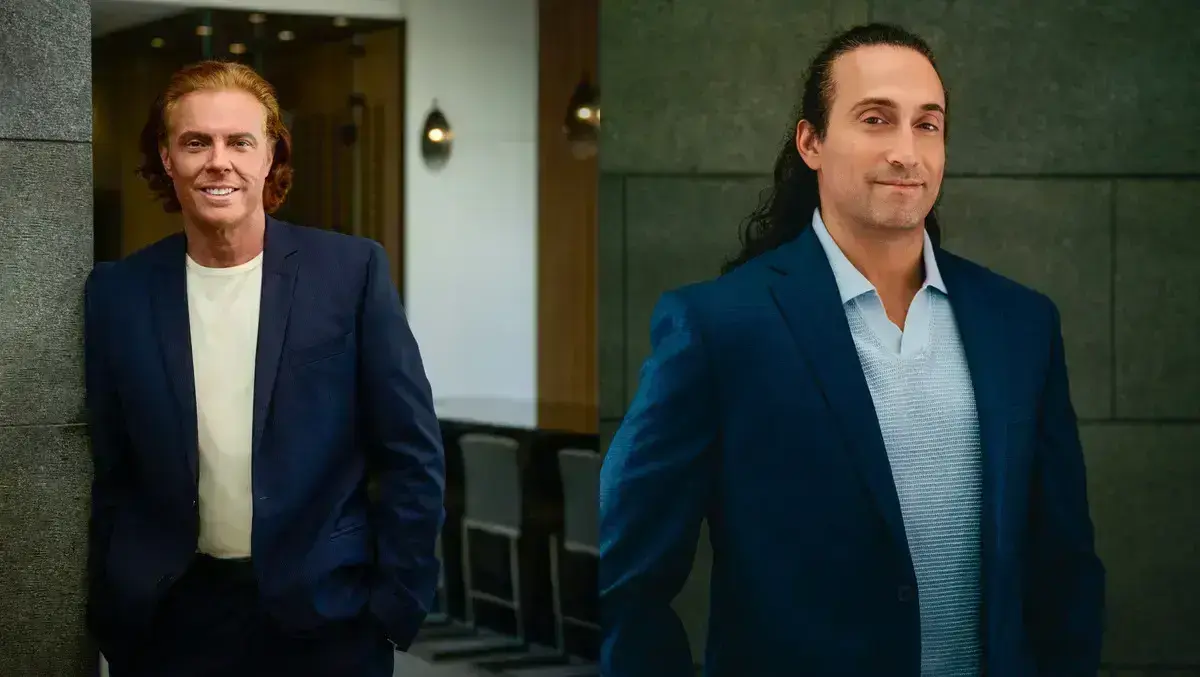
Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security, said phishing is becoming more automated and harder for conventional protections to catch.
"Phishing attacks are no longer simple email scams; they are highly automated, AI-driven operations designed to trick users into handing over sensitive credentials and information," said Guccione, Chief Executive Officer and Co-founder of Keeper Security. "When an adversary sets up a look-alike domain, form field or unofficial login portal, traditional security controls often fail to identify the threat until the damage is done. By embedding zero-knowledge AI into our browser extension, Keeper stops credential harvesting at the point of entry, giving individuals and organisations greater security and control."
Keeper said the feature uses what it describes as a zero-knowledge architecture, meaning data examined by the AI model remains on the user's device. In practice, that approach is intended to address a long-running tension in security software between broader inspection of user activity and privacy concerns over where that information is processed and stored.
Phishing detection in browsers has become a more active area for security vendors as attackers use generative AI tools to create more convincing fake pages and domain names. These campaigns often mimic trusted brands, online services and corporate login portals, making them difficult for users to distinguish from genuine sites.
Browser extensions and password managers already sit close to the point where credentials are entered, giving them a natural role in detecting suspicious pages and limiting autofill when a site appears unsafe. Keeper's latest release builds on that position by adding a warning step before a password is submitted.
Privacy focus
Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security, said the product was designed to keep analysis on the local device while preserving the company's existing privacy model.
"Security controls have to work at machine speed, and they cannot come at the expense of the zero-knowledge guarantees our customers depend on," said Lurey. "We engineered this AI engine to execute entirely on the local device using the customer's private key. It delivers continuous, proactive verification of web assets, ensuring that autofill is protected against sophisticated domain spoofing without creating a privacy trade-off."
The launch adds another browser-based security layer to Keeper's broader identity and access product line, as vendors across the sector respond to the growing use of stolen credentials in attacks on businesses and consumers.